01 April 2018

DARPA wants new ideas for autonomous drone swarms


The Defense Department’s research wing is serious about putting drones into action, not just one by one but in coordinated swarms. The Offensive Swarm-Enabled Tactics program is kicking off its second “sprint,” a period of solicitation and rapid prototyping of systems based around a central theme. This spring sprint is all about “autonomy.”

The idea is to collect lots of ideas on how new technology, be it sensors, software, or better propeller blades, can enhance the ability of drones to coordinate and operate as a collective.

Specifically, swarms of 50 will need to “isolate an urban objective” within half an hour or so by working together with each other and ground-based robot. That at least is the “operational backdrop” that should guide prospective entrants in their decision whether their tech is applicable.

So a swarm of drones that seed a field faster than a tractor, while practical for farmers, isn’t really something the Pentagon is interested in here. On the other hand, if you can sell that idea as a swarm of drones dropping autonomous sensors on an urban battlefield, they might take a shine to it.

But you could also simply demonstrate how using a compact ground-based lidar system could improve swarm coordination at low cost and without using visible light. Or maybe you’ve designed a midair charging system that lets a swarm perk up flagging units without human intervention.

Those are pretty good ideas, actually — maybe I’ll run them by the program manager, Timothy Chung, when he’s on stage at our Robotics event in Berkeley this May. Chung also oversees the Subterranean Challenge and plenty more at DARPA. He looks like he’s having a good time in the video explaining the ground rules of this new sprint:

You don’t have to actually have 50 drones to take part — there are simulators and other ways of demonstrating value. More information on the program and how to submit your work for consideration can be found at the FBO page.


Read Full Article

Facebook plans crackdown on ad targeting by email without consent


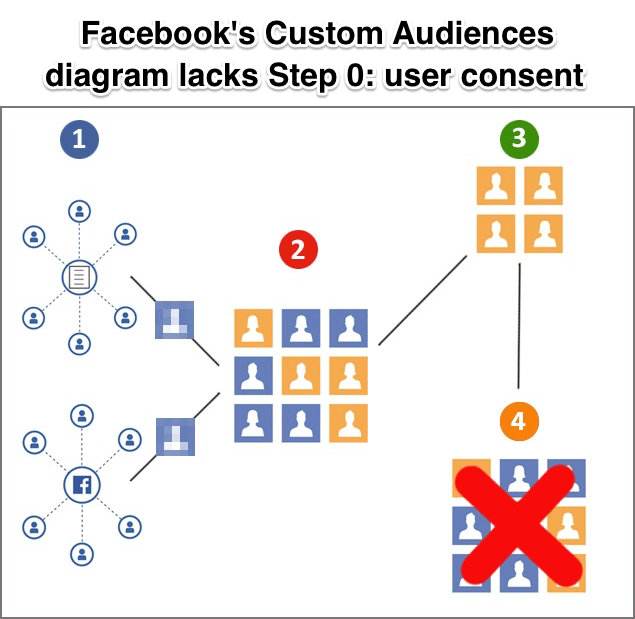
Facebook is scrambling to add safeguards against abuse of user data as it reels from backlash over the Cambridge Analytica scandal. Now TechCrunch has learned Facebook will launch a certification tool that demands that marketers guarantee email addresses used for ad targeting were rightfully attained. This new Custom Audiences certification tool was described by Facebook representatives to their marketing clients, according to two sources. Facebook will also prevent the sharing of Custom Audience data across Business accounts.

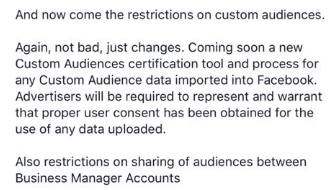
This snippet of a message sent by a Facebook rep to a client notes that “for any Custom Audiences data imported into Facebook, Advertisers will be required to represent and warrant that proper user content has been obtained.”

Once shown the message, Facebook spokesperson Elisabeth Diana told TechCrunch “I can confirm there is a permissions tool that we’re building.” It will require that advertisers and the agencies representing them pledge that “I certify that I have permission to use this data”, she said.

Diana noted that “We’ve always had terms in place to ensure that advertisers have consent for data they use but we’re going to make that much more prominent and educate advertisers on the way they can use the data.” The change isn’t in response to a specific incident, but Facebook does plan to re-review the way it works with third-party data measurement firms to ensure everything is responsibly used. This is a way to safeguard data” Diana concluded.The company declined to specify whether it’s ever blocked usage of a Custom Audience because it suspected the owner didn’t have user consent. ”

The social network is hoping to prevent further misuse of ill-gotten data after Dr. Aleksandr Kogan’s app that pulled data on 50 million Facebook users was passed to Cambridge Analytica in violation of Facebook policy. That sordid data is suspected to have been used by Cambridge Analytica to support the Trump and Brexit campaigns, which employed Custom Audiences to reach voters.

Facebook launched Custom Audiences back in 2012 to let businesses upload hashed lists of their customers email addresses or phone numbers, allowing advertisers to target specific people instead of broad demographics. Custom Audiences quickly became one of Facebook’s most powerful advertising options because businesses could easily reach existing customers to drive repeat sales. The Custom Audiences terms of service require that businesses have “provided appropriate notice to and secured any necessary consent from the data subjects” to attain and use these people’s contact info.

But just like Facebook’s policy told app developers like Kogan not to sell, share, or misuse data they collected from Facebook users, the company didn’t go further to enforce this rule. It essentially trusted that the fear of legal repercussions or suspension on Facebook would deter violations of both its app data privacy and Custom Audiences consent policies. With clear financial incentives to bend or break those rules and limited effort spent investigating to ensure compliance, Facebook left itself and its users open to exploitation.

Last week Facebook banned the use of third-party data brokers like Experian and Acxiom for ad targeting, closing a marketing featured called Partner Categories. Facebook is believed to have been trying to prevent any ill-gotten data from being laundered through these data brokers and then directly imported to Facebook to target users. But that left open the option for businesses to compile illicit data sets or pull them from data brokers, then upload them to Facebook as Custom Audiences by themselves.

The Custom Audiences certification tool could close that loophole. It’s still being built, so Facebook wouldn’t say exactly how it will work. I asked if Facebook would scan uploaded user lists and try to match them against a database of suspicious data, but for now it sounds more like Facebook will merely require a written promise.

Meanwhile, barring the sharing of Custom Audiences between Business Accounts might prevent those with access to email lists from using them to promote companies unrelated to the one to which users gave their email address. Facebook declined to comment on how the new ban on Custom Audience sharing would work.

Now Facebook must find ways to thwart misuse of its targeting tools and audit anyone it suspects may have already violated its policies. Otherwise it may receive the ire of privacy-conscious users and critics, and strengthen the case for substantial regulation of its ads (though regulation could end up protecting Facebook from competitors who can’t afford compliance). Still the question remains why it took such a massive data privacy scandal for Facebook to take a tougher stance on requiring user consent for ad targeting. And given that written promises didn’t stop Kogan or Cambridge Analytica from misusing data, why would they stop advertisers bent on boosting profits?

For more on Facebook’s recent scandals, check out TechCrunch’s coverage:


Read Full Article

Facebook plans crackdown on ad targeting by email without consent


Facebook is scrambling to add safeguards against abuse of user data as it reels from backlash over the Cambridge Analytica scandal. Now TechCrunch has learned Facebook will launch a certification tool that demands that marketers guarantee email addresses used for ad targeting were rightfully attained. This new Custom Audiences certification tool was described by Facebook representatives to their marketing clients, according to two sources. Facebook will also prevent the sharing of Custom Audience data across Business accounts.

This snippet of a message sent by a Facebook rep to a client notes that “for any Custom Audiences data imported into Facebook, Advertisers will be required to represent and warrant that proper user content has been obtained.”

Once shown the message, Facebook spokesperson Elisabeth Diana told TechCrunch “I can confirm there is a permissions tool that we’re building.” It will require that advertisers and the agencies representing them pledge that “I certify that I have permission to use this data”, she said.

Diana noted that “We’ve always had terms in place to ensure that advertisers have consent for data they use but we’re going to make that much more prominent and educate advertisers on the way they can use the data.” The change isn’t in response to a specific incident, but Facebook does plan to re-review the way it works with third-party data measurement firms to ensure everything is responsibly used. This is a way to safeguard data” Diana concluded.The company declined to specify whether it’s ever blocked usage of a Custom Audience because it suspected the owner didn’t have user consent. ”

The social network is hoping to prevent further misuse of ill-gotten data after Dr. Aleksandr Kogan’s app that pulled data on 50 million Facebook users was passed to Cambridge Analytica in violation of Facebook policy. That sordid data is suspected to have been used by Cambridge Analyica to support the Trump and Brexit campaigns, which employed Custom Audiences to reach voters.

Facebook launched Custom Audiences back in 2012 to let businesses upload hashed lists of their customers email addresses or phone numbers, allowing advertisers to target specific people instead of broad demographics. Custom Audiences quickly became one of Facebook’s most powerful advertising options because businesses could easily reach existing customers to drive repeat sales. The Custom Audiences terms of service require that businesses have “provided appropriate notice to and secured any necessary consent from the data subjects” to attain and use these people’s contact info.

But just like Facebook’s policy told app developers like Kogan not to sell, share, or misuse data they collected from Facebook users, the company didn’t go further to enforce this rule. It essentially trusted that the fear of legal repercussions or suspension on Facebook would deter violations of both its app data privacy and Custom Audiences consent policies. With clear financial incentives to bend or break those rules and limited effort spent investigating to ensure compliance, Facebook left itself and its users open to exploitation.

Last week Facebook banned the use of third-party data brokers like Experian and Acxiom for ad targeting, closing a marketing featured called Partner Categories. Facebook is believed to have been trying to prevent any ill-gotten data from being laundered through these data brokers and then directly imported to Facebook to target users. But that left open the option for businesses to compile illicit data sets or pull them from data brokers, then upload them to Facebook as Custom Audiences by themselves.

The Custom Audiences certification tool could close that loophole. It’s still being built, so Facebook wouldn’t say exactly how it will work. I asked if Facebook would scan uploaded user lists and try to match them against a database of suspicious data, but for now it sounds more like Facebook will merely require a written promise.

Meanwhile, barring the sharing of Custom Audiences between Business Accounts might prevent those with access to email lists from using them to promote companies unrelated to the one to which users gave their email address. Facebook declined to comment on how the new ban on Custom Audience sharing would work.

Now Facebook must find ways to thwart misuse of its targeting tools and audit anyone it suspects may have already violated its policies. Otherwise it may receive the ire of privacy-conscious users and critics, and strengthen the case for substantial regulation of its ads (though regulation could end up protecting Facebook from competitors who can’t afford compliance). Still the question remains why it took such a massive data privacy scandal for Facebook to take a tougher stance on requiring user consent for ad targeting. And given that written promises didn’t stop Kogan or Cambridge Analytica from misusing data, why would they stop advertisers bent on boosting profits?

For more on Facebook’s recent scandals, check out TechCrunch’s coverage:


Read Full Article

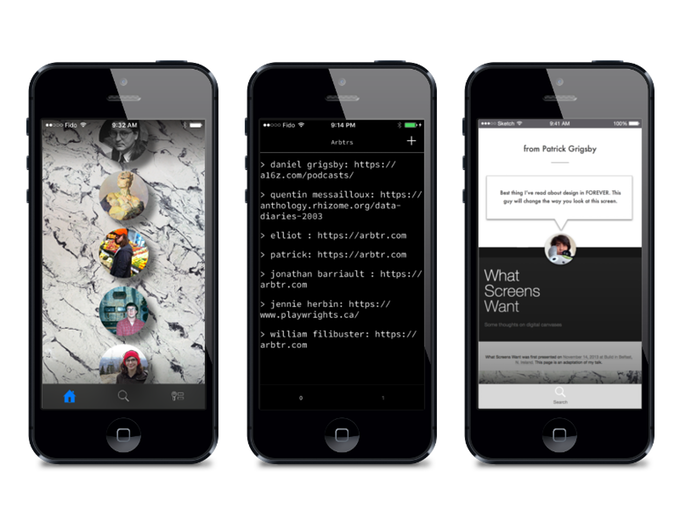
Arbtr wants to create an anti-feed where users can only share one thing at a time


At a time when the models of traditional social networks are being questioned, it’s more important than ever to experiment with alternatives. Arbtr is a proposed social network that limits users to sharing a single thing at any given time, encouraging “ruthless self-editing” and avoiding “nasty things” like endless feeds filled with trivial garbage.

It’s seeking funds on Kickstarter and could use a buck or two. I plan to.

Now, I know what you’re thinking. “Why would I give money to maybe join a social network eventually that might not have any of my friends on it on it? That is, if it ever even exists?” Great question.

The answer is: how else do you think we’re going to replace Facebook? Someone with a smart, different idea has to come along and we have to support them. If we won’t spare the cost of a cup of coffee for a purpose like that, then we deserve the social networks we’ve got. (And if I’m honest, I’ve had very similar ideas over the last few years and I’m eager to see how they might play out in reality.)

The fundamental feature is, of course, the single-sharing thing. You can only show off one item at a time, and when you post a new one, the old one (and any discussion, likes, etc) will be deleted. There will be options to keep logs of these things, and maybe premium features to access them (or perhaps metrics), but the basic proposal is, I think, quite sound — at the very least, worth trying.

Some design ideas for the app. I like the text one but it does need thumbnails.

If you’re sharing less, as Arbtr insists you will, then presumably you’ll put more love behind those things you do share. Wouldn’t that be nice?

We’re in this mess because we bought wholesale the idea that the more you share, the more connected you are. Now that we’ve found that isn’t the case – and in fact we were in effect being fattened for a perpetual slaughter — I don’t see why we shouldn’t try something else.

Will it be Arbtr? I don’t know. Probably not, but we’ve got a lot to gain by giving ideas like this a shot.


Read Full Article

31 March 2018

Knitting machines power up with computer-generated patterns for 3D shapes


At last, a use for that industrial knitting machine you bought at a yard sale! Carnegie Mellon researchers have created a method that generates knitting patterns for arbitrary 3D shapes, opening the possibility of “on-demand knitting.” Think 3D printing, but softer.

The idea is actually quite compelling for those of us who are picky about their knitwear. How often have we picked up a knit cap, glove, or scarf only to find it too long, too short, too tight, too loose, etc?

If you fed your sartorial requirements (a 3D mesh) into this system from James McCann and students at CMU’s Textiles Lab, it could quickly spit out a pattern that a knitting machine could follow easily yet is perfectly suited for your purposes.

This has to be done carefully — the machines aren’t the same as human knitters, obviously, and a poorly configured pattern might lead to yarn breaking or jamming the machine. But it’s a lot better than having to build that pattern purl by purl.

With a little more work, “Knitting machines could become as easy to use as 3D printers,” McCann said in a CMU news release.

Of course, it’s unlikely you’ll have one of your own. But maker spaces and designer ateliers (I believe that’s the term) will be more likely to if it’s this easy to create new and perfectly sized garments with them.

McCann and his team will be presenting their research at SIGGRAPH this summer.


Read Full Article

Who gains from Facebook’s missteps?


When Facebook loses, who wins?

That’s a question for startups that may be worth contemplating following Facebook’s recent stock price haircut. The company’s valuation has fallen by around $60 billion since the Cambridge Analytica scandal surfaced earlier this month and the #DeleteFacebook campaign gained momentum.

That’s a steep drop, equal to about 12 percent of the company’s market valuation, and it’s a decline Facebook appears to be suffering alone. As its shares fell over the past couple of weeks, stocks of other large-cap tech and online media companies have been much flatter.

So where did the money go? It’s probably a matter of perspective. For a Facebook shareholder, that valuation is simply gone. And until executives’ apologies resonate and users’ desire to click and scroll overcomes their privacy fears, that’s how it is.

An alternate view is that the valuation didn’t exactly disappear. Investors may still believe the broad social media space is just as valuable as it was a couple of weeks ago. It’s just that less of that pie should be the exclusive domain of Facebook.

If one takes that second notion, then the possibilities for who could benefit from Facebook’s travails start to get interesting. Of course, there are public market companies, like Snap or Twitter, that might pick up traffic if the #DeleteFacebook movement gains momentum without spreading to other big brands. But it’s in the private markets where we see the highest number of potential beneficiaries of Facebook’s problems.

In an effort to come up with some names, we searched through Crunchbase for companies in social media and related areas. The resulting list includes companies that have raised good-sized rounds in the past couple of years and could conceivably see gains if people cut back on using Facebook or owning its stock.

Of course, people use Facebook for different things (posting photos, getting news, chatting with friends and so on), so we lay out a few categories of potential beneficiaries of a Facebook backlash.

Messaging

Facebook has a significant messaging presence, but it hasn’t been declared the winner. Alternatives like Snap, LINE, WeChat and plain old text messages are also massively popular.

That said, what’s bad for Messenger and Facebook-owned WhatsApp is probably good for competitors. And if more people want to do less of their messaging on Facebook, it helps that there are a number of private companies ready to take its place.

Crunchbase identified six well-funded messaging apps that could fit the bill (see list). Collectively, they’ve raised well over $2 billion — if one includes the $850 million initial coin offering by Telegram.

Increasingly, these private messaging startups are focused on privacy and security, including Wickr, the encrypted messaging tool that has raised more than $70 million, and Silent Circle, another encrypted communications provider that has raised $130 million.

Popular places to browse on a screen

People who cut back on Facebook may still want to spend hours a day staring at posts on a screen. So it’s likely they’ll start staring at something else that’s content-rich, easy-to-navigate and somewhat addictive.

Luckily, there are plenty of venture-backed companies that fit that description. Many of these are quite mature at this point, including Pinterest for image collections, Reddit for post and comment threads and Quora for Q&A (see list).

Granted, these will not replace the posts keeping you up to date on the life events of family and friends. But they could be a substitute for news feeds, meme shares and other non-personal posts.

Niche content

A decline in Facebook usage could translate into a rise in traffic for a host of niche content and discussion platforms focused on sports, celebrities, social issues and other subjects.

Crunchbase News identified at least a half-dozen that have raised funding in recent quarters, which is just a sampling of the total universe. Selected startups run the gamut from The Players’ Tribune, which features first-hand accounts for top athletes, to Medium, which seeks out articles that resonate with a wide audience.

Niche sites also provide a more customized forum for celebrities, pundits and subject-matter experts to engage directly with fans and followers.

Community and engagement

People with common interests don’t have to share them on Facebook. There are other places that can offer more tailored content and social engagement.

In recent years, we’ve seen an increase in community and activity-focused social apps gain traction. Perhaps the most prominent is Nextdoor, which connects neighbors for everything from garage sales to crime reports. We’re also seeing some upstarts focused on creating social networks for interest groups. These include Mighty Networks and Amino Apps.

Though some might call it a stretch, we also added to the list WeWork, recent acquirer of Meetup, and The Guild, two companies building social networks in the physical world. These companies are encouraging people to come out and socially network with other people (even if just means sitting in a room with other people staring at a screen).

Watch where the money goes

Facebook’s latest imbroglio is still too recent to expect a visible impact in the startup funding arena. But it will be interesting to watch in the coming months whether potential rivals in the above categories raise a lot more cash and attract more users.

If there’s demand, there’s certainly no shortage of supply on the investor front. The IPO window is wide open, and venture investors are sitting on record piles of dry powder. It hasn’t escaped notice, either, that social media offerings, like Facebook, LinkedIn and Snap, have generated the biggest exit total of any VC-funded sector.

Moreover, those who’ve argued that it’s too late for newcomers have a history of being proven wrong. After all, that’s what people were saying about would-be competitors to MySpace in 2005, not long before Facebook made it big.


Read Full Article

Google needs your help finding Waldo


At some point in the not-so-distant past, April Fools was about pranks and hoaxes, but given that we apparently have enough of those on the web, the day has somehow morphed into a celebration of random jokey things. This year’s Google Maps gag is no exception.

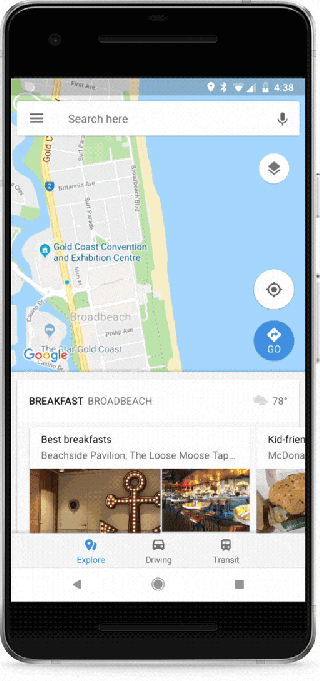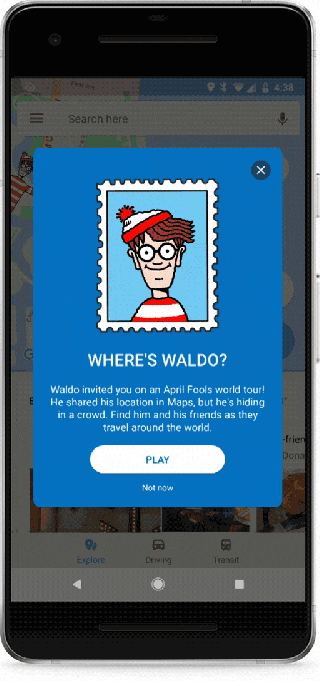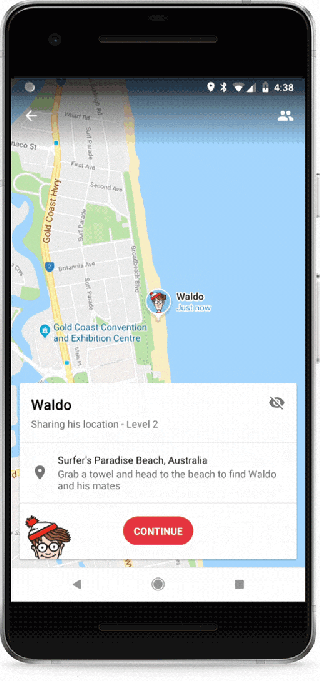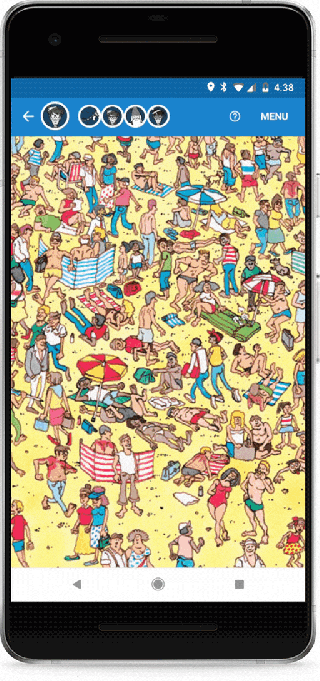
Starting today, when you open Google Maps on your phone or desktop, you’ll see Waldo in his trademark red and white sweater, waving at you you from the side of your screen. That’s because Waldo is sharing his location with you for the next few days and he really wants to be found (or not… I’m never quite sure about what Waldo’s real motivations are…). You can also ask the Google Assistant “Hey Google. Where’s Waldo?”

Then, when you click on Waldo in the map, you get to see a standard “Where is Waldo” image and your job is to find him, as well as Woof, Wenda, Wizard Whitebeard and Odlaw.

Now if Google had wanted to make this a real April Fools joke, it would’ve announced this and then never released it or just shown you a standard “Where is Waldo” image without Waldo. That way, it would’ve driven everybody mad. But I’m pretty sure it’s for real, so head over to Google Maps and give it a try.


Read Full Article

The 4 Best NAS for Home Media Servers and Shared Storage

How to Disable UEFI to Dual Boot Any Operating System


Have you ever tried to install a second operating system alongside Windows? Depending on what you tried to install, you might have encountered the UEFI Secure Boot feature. If Secure Boot doesn’t recognize the code you’re trying to install, it will stop you. Secure Boot is handy for preventing malicious code running on your system. But it also stops you booting some legitimate operating systems, like Kali Linux, Android x86, or TAILS.

But there is a way around it. This short guide will show you how to disable UEFI Secure Boot to let you dual boot any operating system you like.

UEFI Secure Boot

Let’s take a second to consider precisely how Secure Boot keeps your system safe.

Secure Boot is a feature of the Unified Extensible Firmware Interface (UEFI). UEFI itself is the replacement for the BIOS interface found on many devices. UEFI is a more advanced firmware interface with many more customization and technical options.

Computer Security, UEFI, BIOS, Dual Boot

Secure Boot is something of a security gate. It analyzes code before you execute it on your system. If the code has a valid digital signature, Secure Boot lets it through the gate. If the code has an unrecognized digital signature, Secure Boot blocks it from running, and the system will require a restart.

At times, code that you know is safe, and comes from a reliable source, might not have a digital signature in the Secure Boot database.

For example, you can download numerous Linux distributions directly from their developer site, even verifying the distribution checksum to check for tampering. But even with that confirmation, Secure Boot will still reject some operating systems and other types of code (such as drivers and hardware).

How to Disable Secure Boot

Now, we don’t advise disabling Secure Boot lightly. It really does keep you safe (check out the Secure Boot vs. Petya Ransomware video below, for example), especially from some of the nastier malware variants like rootkits and bootkits (others would contend it was the security measure to stop Windows pirating). That said, sometimes it gets in the way.

Please note that turning Secure Boot back on may require a BIOS reset. This does not cause your system to lose any data. It does, however, remove any custom BIOS settings. Moreover, there are some examples where users are permanently no longer able to turn Secure Boot, so please bare that in mind.

Okay, here’s what you do:

  1. Turn your computer off. Then, turn it back on and press the BIOS enter key during the boot process. This varies between hardware types, but is generally F1, F2, F12, Esc, or Del; Windows users can hold Shift while selecting Restart to enter the Advanced Boot Menu. Then select Troubleshoot > Advanced Options: UEFI Firmware Settings.
  2. Find the Secure Boot. If possible, set it to Disabled. The Secure Boot option is usually found in the Security tab, Boot tab, or Authentication tab.
  3. Save and Exit. Your system will reboot.

You have successfully disabled Secure Boot. Feel free you grab your nearest previously unbootable USB drive and finally explore the operating system. Kali Linux and TAILS are a great places to start.

How to Re-Enable Secure Boot

Of course, you might want to turn Secure Boot back on. After all, it does help protect against nefarious malware and other unauthorized code. If you directly install an unsigned operating system, you’ll need to remove all traces before attempting to turn Secure Boot back on. Otherwise, the process will fail.

  1. Uninstall any unsigned operating systems or hardware installed when Secure Boot was disabled.
  2. Turn your computer off. Then, turn it back on and press the BIOS enter key during the boot process. This varies between hardware types, but is generally F1, F2, F12, Esc, or Del; Windows users can hold Shift while selecting Restart to enter the Advanced Boot Menu.
  3. Find the Secure Boot If possible, set it to Enabled. The Secure Boot option is usually found in the Security tab, Boot tab, or Authentication tab.
  4. If Secure Boot doesn’t enable, try to Reset your BIOS to factory settings. Once you restore factory settings, attempt to enable Secure Boot again.
  5. Save and Exit. Your system will reboot.
  6. In the event the system fails to boot, disable Secure Boot again.

Troubleshooting Secure Boot Enable Failure

There are a few small fixes we can try to get your system booting with Secure Boot enabled.

  • Make sure to turn UEFI settings on in the BIOS menu; this also means making sure Legacy Boot Mode and equivalents are off.
  • Check your drive partition type. UEFI requires GPT partition style, rather than the MBR used by Legacy BIOS setups. To do this, type Computer Management in your Windows Start menu search bar and select the best match. Select Disk Management from the menu. Now, find your primary drive, right-click, and select Properties. Now, select the Volume Your partition style is listed here.
    • If you need to switch from MBR to GPT there is only one option to change the partition style: back up your data and wipe the drive.
  • Some firmware managers have the option to Restore Factory Keys, usually found in the same tab as the other Secure Boot options. If you have this option, restore the Secure Boot factory keys. Then Save and Exit, and reboot.

Computer Security, UEFI, BIOS, Dual Boot

Trusted Boot

Trusted Boot picks up where Secure Boot stops, but really only applies to the Windows 10 digital signature. Once UEFI Secure Boot passes the baton, Trusted Boot verifies every other aspect of Windows, including drivers, startup files, and more.

Much like Secure Boot, if Trusted Boot finds a corrupted or malicious component, it refuses to load. However, unlike Secure Boot, Trusted Boot can at times automatically repair the issue at hand, depending on the severity. The below image explains a little more about where Secure Boot and Trusted Boot fit together in the Windows boot process.

Computer Security, UEFI, BIOS, Dual Boot

To Secure Boot or Not?

Disabling Secure Boot is somewhat risky. Depending on who you ask, you’re potentially putting your system security at risk.

Secure Boot is arguably more useful than ever at the current time. Bootloader attacking ransomware is very real. Rootkits and other particularly nasty malware variants are also out in the wild. Secure Boot provides UEFI systems with an extra level of system validation to give you peace of mind.


Read Full Article

4 Digital Hacks for Your Bullet Journal That Always Work

Chinese police foil drone-flying phone smugglers at Hong Kong border


Dozens of high-tech phone smugglers have been apprehended by Chinese police, who twigged to the scheme to send refurbished iPhones into the country from Hong Kong via drone — but not the way you might think.

China’s Legal Daily reported the news (and Reuters noted shortly after) following a police press conference; it’s apparently the first cross-border drone-based smuggling case, so likely of considerable interest.

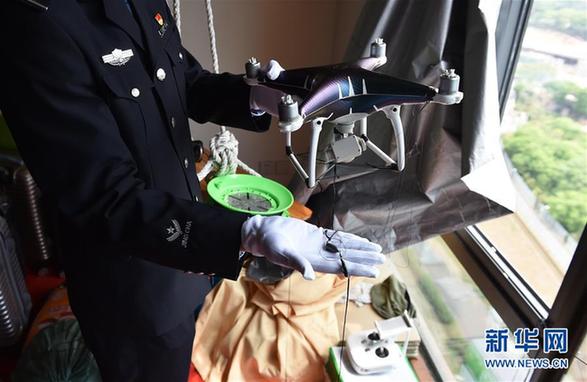
Although the methods used by the smugglers aren’t described, a picture emerges from the details. Critically, in addition to the drones themselves, which look like DJI models with dark coverings, police collected some long wires — more than 600 feet long.

Small packages of 10 or so phones were sent one at a time, and it only took “seconds” to get them over the border. That pretty much rules out flying the drone up and over the border repeatedly — leaving aside that landing a drone in pitch darkness on the other side of a border fence (or across a body of water) would be difficult to do once or twice, let alone dozens of times, the method is also inefficient and and risky.

But really, the phones only need to clear the border obstacle. So here’s what you do:

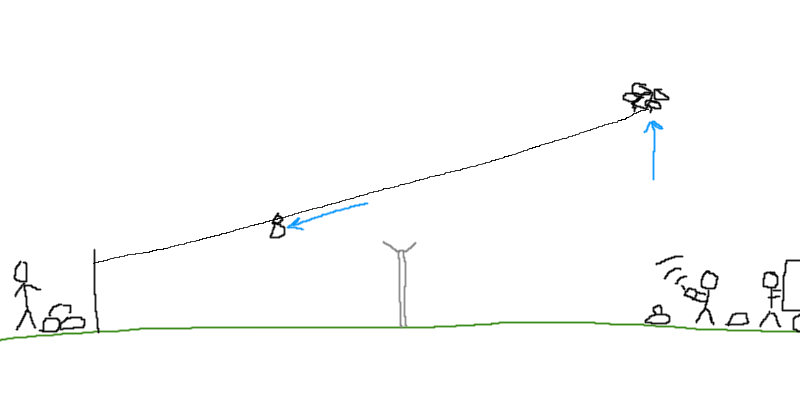
Send the drone over once with all cable attached. Confederates on the other side attach the cable to a fixed point, say 10 or 15 feet off the ground. Drone flies back unraveling the cable, and lands some distance onto the Hong Kong side. Smugglers attach a package of 10 phones to the cable with a carabiner, and the drone flies straight up. When the cable reaches a certain tension, the package slides down the cable, clearing the fence. The drone descends, and you repeat.

I’ve created a highly professional diagram to illustrate this technique (feel free to reuse):

It’s not 100 percent to scale. The far side might have to be high enough that the cable doesn’t rest on the fence, if there is one, or not to drag in the water if that’s the case. Not sure about that part.

Anyway, it’s quite smart. You get horizontal transport basically for free, and the drone only has to do what it does best: go straight up. Two wires were found, and the police said up to 15,000 phones might be sent across in a night. Assuming 10 phones per trip, and say 20 seconds per flight, that works out to 1,800 phones per hour per drone, which sounds about right. Probably this kind of thing is underway at more than a few places around the world.


Read Full Article

The real threat to Facebook is the kool-aid turning sour


These kinds of leaks didn’t happen when I started reporting on Facebook eight years ago. It was a tight-knit cult convinced of its mission to connect everyone, but with the discipline of a military unit where everyone knew loose lips sink ships. Motivational posters with bold corporate slogans dotted its offices, rallying the troops. Employees were happy to be evangelists.

But then came the fake news, News Feed addiction, violence on Facebook Live, cyberbullying, abusive ad targeting, election interference, and most recently the Cambridge Analytica app data privacy scandals. All the while, Facebook either willfully believed the worst case scenarios could never come true, was naive to their existence, or calculated the benefits and growth outweighed the risks. And when finally confronted, Facebook often dragged its feet before admitting the extent of the problems.

Inside the social network’s offices, the bonds began to fray. Slogans took on sinister second meanings. The kool-aid tasted different.
Some hoped they could right the ship but couldn’t. Some craved the influence and intellectual thrill of running one of humanity’s most popular inventions, but now question if that influence and their work is positive. Others surely just wanted to collect salaries, stock, and resume highlights but lost the stomach for it.

Now the convergence of scandals has come to a head in the form of constant leaks.

The Trouble Tipping Point

The more benign leaks merely cost Facebook a bit of competitive advantage. We’ve learned it’s building a smart speaker, a standalone VR headset, and a Houseparty split-screen video chat clone.

Yet policy-focused leaks have exacerbated the backlash against Facebook, putting more pressure on the conscience of employees. As blame fell to Facebook for Trump’s election, word of Facebook prototyping a censorship tool for operating in China escaped, triggering questions about its respect for human rights and free speech. Facebook’s content rulebook got out alongside disturbing tales of the filth the company’s contracted moderators have to sift through. Its ad targeting was revealed to be able to pinpoint emotionally vulnerable teens.

In recent weeks, the leaks have accelerated to a maddening pace in the wake of Facebook’s soggy apologies regarding the Cambridge Analytica debacle. Its weak policy enforcement left the door open to exploitation of data users gave third-party apps, deepening the perception that Facebook doesn’t care about privacy.
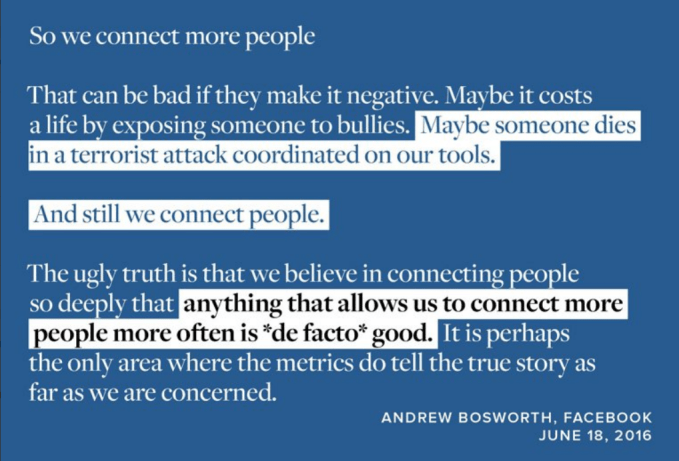
And it all culminated with BuzzFeed publishing a leaked “growth at all costs” internal post from Facebook VP Andrew “Boz” Bosworth that substantiated people’s worst fears about the company’s disregard for user safety in pursuit of world domination. Even the ensuing internal discussion about the damage caused by leaks and how to prevent them…leaked.

But the leaks are not the disease, just the symptom. Sunken morale is the cause, and it’s dragging down the company. Former Facebook employee and Wired writer Antonio Garcia Martinez sums it up, saying this kind of vindictive, intentionally destructive leak fills Facebook’s leadership with “horror”:

And that sentiment was confirmed by Facebook’s VP of News Feed Adam Mosseri, who tweeted that leaks “create strong incentives to be less transparent internally and they certainly slow us down”, and will make it tougher to deal with the big problems.

Those thoughts weigh heavy on Facebook’s team. A source close to several Facebook executives tells us they feel “embarrassed to work there” and are increasingly open to other job opportunities. One current employee told us to assume anything certain execs tell the media is “100% false”.

If Facebook can’t internally discuss the problems it faces without being exposed, how can it solve them?

Implosion

The consequences of Facebook’s failures are typically pegged as external hazards.

You might assume the government will finally step in and regulate Facebook. But the Honest Ads Act and other rules about ads transparency and data privacy could end up protecting Facebook by being simply a paperwork speed bump for it while making it tough for competitors to build a rival database of personal info. In our corporation-loving society, it seems unlikely that the administration would go so far as to split up Facebook, Instagram, and WhatsApp — one of the few feasible ways to limit the company’s power.
Users have watched Facebook go make misstep after misstep over the years, but can’t help but stay glued to its feed. Even those who don’t scroll rely on it as fundamental utility for messaging and login on other sites. Privacy and transparency are too abstract for most people to care about. Hence, first-time Facebook downloads held steady and its App Store rank actually rose in the week after the Cambridge Analytica fiasco broke. In regards to the #DeleteFacebook movement, Mark Zuckerberg himself said “I don’t think we’ve seen a meaningful number of people act on that.” And as long as they’re browsing, advertisers will keep paying Facebook to reach them.

That’s why the greatest threat of the scandal convergence comes from inside. The leaks are the canary in the noxious blue coal mine.

Can Facebook Survive Slowing Down?

If employees wake up each day unsure whether Facebook’s mission is actually harming the world, they won’t stay. Facebook doesn’t have the same internal work culture problems as some giants like Uber. But there are plenty of other tech companies with less questionable impacts. Some are still private and offer the chance to win big on an IPO or acquisition. At the very least, those in the Bay could find somewhere to work without a spending hours a day on the traffic-snarled 101 freeway.

If they do stay, they won’t work as hard. It’s tough to build if you think you’re building a weapon. Especially if you thought you were going to be making helpful tools. The melancholy and malaise set in. People go into rest-and-vest mode, living out their days at Facebook as a sentence not an opportunity. The next killer product Facebook needs a year or two from now might never coalesce.

And if they do work hard, a culture of anxiety and paralysis will work against them. No one wants to code with their hands tied, and some would prefer a less scrutinized environment. Every decision will require endless philosophizing and risk-reduction. Product changes will be reduced to the lowest common denominator, designed not to offend or appear too tyrannical.
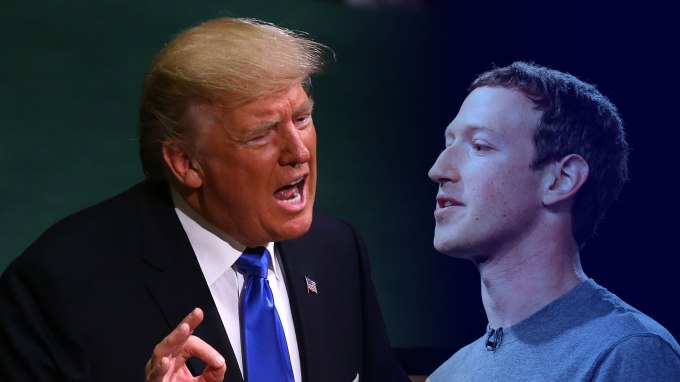
Source: Volkan Furuncu/Anadolu Agency + David Ramos/Getty Images

In fact, that’s partly how Facebook got into this whole mess. A leak by an anonymous former contractor led Gizmodo to report Facebook was suppressing conservative news in its Trending section. Terrified of appearing liberally biased, Facebook reportedly hesitated to take decisive action against fake news. That hands-off approach led to the post-election criticism that degraded morale and pushed the growing snowball of leaks down the mountain.

It’s still rolling.
How to stop morale’s downward momentum will be one of Facebook’s greatest tests of leadership. This isn’t a bug to be squashed. It can’t just roll back a feature update. And an apology won’t suffice. It will have to expel or reeducate the leakers and disloyal without instilling a witchunt’s sense of dread. Compensation may have to jump upwards to keep talent aboard like Twitter did when it was floundering. Its top brass will need to show candor and accountability without fueling more indiscretion. And it may need to make a shocking, landmark act of humility to convince employees its capable of change.

This isn’t about whether Facebook will disappear tomorrow, but whether it will remain unconquerable for the forseeable future.

Growth has been the driving mantra for Facebook since its inception. No matter how employees are evaluated, it’s still the underlying ethos. Facebook has poised itself as a mission-driven company. The implication was always that connecting people is good so connecting more people is better. The only question was how to grow faster.

Now Zuckerberg will have to figure out how to get Facebook to cautiously foresee the consequences of what it says and does while remaining an appealing place to work. “Move slow and think things through” just doesn’t have the same ring to it.


Read Full Article
The real threat to Facebook is the kool-aid turning sour


These kinds of leaks didn’t happen when I started reporting on Facebook eight years ago. It was a kool-aid cult convinced of its mission to connect everyone, but with the discipline of a military unit where everyone knew loose lips sink ships. Motivational posters with bold corporate slogans dotted its offices, rallying the troops. Employees were happy to be evangelists.

But then came the fake news, News Feed addiction, violence on Facebook Live, cyberbullying, abusive ad targeting, election interference, and most recently the Cambridge Analytica app data privacy scandals. All the while, Facebook either willfully believed the worst case scenarios could never come true, was naive to their existence, or calculated the benefits and growth outweighed the risks. And when finally confronted, Facebook often dragged its feet before admitting the extent of the problems.

Inside the social network’s offices, the bonds began to fray. Slogans took on sinister second meanings. The kool-aid tasted different.

Some hoped they could right the ship but couldn’t. Some craved the influence and intellectual thrill of running one of humanity’s most popular inventions, but now question if that influence and their work is positive. Others surely just wanted to collect salaries, stock, and resume highlights but lost the stomach for it.

Now the convergence of scandals has come to a head in the form of constant leaks.

The Trouble Tipping Point

The more benign leaks merely cost Facebook a bit of competitive advantage. We’ve learned it’s building a smart speaker, a standalone VR headset, and a Houseparty split-screen video chat clone.

Yet policy-focused leaks have exacerbated the backlash against Facebook, putting more pressure on the conscience of employees. As blame fell to Facebook for Trump’s election, word of Facebook prototyping a censorship tool for operating in China escaped, triggering questions about its respect for human rights and free speech. Facebook’s content rulebook got out alongside disturbing tales of the filth the company’s contracted moderators have to sift through. Its ad targeting was revealed to be able to pinpoint emotionally vulnerable teens.

In recent weeks, the leaks have accelerated to a maddening pace in the wake of Facebook’s soggy apologies regarding the Cambridge Analytica debacle. Its weak policy enforcement left the door open to exploitation of data users gave third-party apps, deepening the perception that Facebook doesn’t care about privacy.

And it all culminated with BuzzFeed publishing a leaked “growth at all costs” internal post from Facebook VP Andrew “Boz” Bosworth that substantiated people’s worst fears about the company’s disregard for user safety in pursuit of world domination. Even the ensuing internal discussion about the damage caused by leaks and how to prevent them…leaked.

But the leaks are not the disease, just the symptom. Sunken morale is the cause, and it’s dragging down the company. Former Facebook employee and Wired writer Antonio Garcia Martinez sums it up, saying this kind of vindictive, intentionally destructive leak fills Facebook’s leadership with “horror”:

And that sentiment was confirmed by Facebook’s VP of News Feed Adam Mosseri, who tweeted that leaks “create strong incentives to be less transparent internally and they certainly slow us down”, and will make it tougher to deal with the big problems.

Those thoughts weigh heavy on Facebook’s team. A source close to several Facebook executives tells us they feel “embarrassed to work there” and are increasingly open to other job opportunities. One current employee told us to assume anything certain execs tell the media is “100% false”.

If Facebook can’t internally discuss the problems it faces without being exposed, how can it solve them?

Implosion

The consequences of Facebook’s failures are typically pegged as external hazards.

You might assume the government will finally step in and regulate Facebook. But the Honest Ads Act and other rules about ads transparency and data privacy could end up protecting Facebook by being simply a paperwork speed bump for it while making it tough for competitors to build a rival database of personal info. In our corporation-loving society, it seems unlikely that the administration would go so far as to split up Facebook, Instagram, and WhatsApp — one of the few feasible ways to limit the company’s power.

Users have watched Facebook go make misstep after misstep over the years, but can’t help but stay glued to its feed. Even those who don’t scroll rely on it as fundamental utility for messaging and login on other sites. Privacy and transparency are too abstract for most people to care about. Hence, first-time Facebook downloads held steady and its App Store rank actually rose in the week after the Cambridge Analytica fiasco broke. In regards to the #DeleteFacebook movement, Mark Zuckerberg himself said “I don’t think we’ve seen a meaningful number of people act on that.” And as long as they’re browsing, advertisers will keep paying Facebook to reach them.

That’s why the greatest threat of the scandal convergence comes from inside. The leaks are the canary in the noxious blue coal mine.

Can Facebook Survive Slowing Down?

If employees wake up each day unsure whether Facebook’s mission is actually harming the world, they won’t stay. Facebook doesn’t have the same internal work culture problems as some giants like Uber. But there are plenty of other tech companies with less questionable impacts. Some are still private and offer the chance to win big on an IPO or acquisition. At the very least, those in the Bay could find somewhere to work without a spending hours a day on the traffic-snarled 101 freeway.

If they do stay, they won’t work as hard. It’s tough to build if you think you’re building a weapon. Especially if you thought you were going to be making helpful tools. The melancholy and malaise set in. People go into rest-and-vest mode, living out their days at Facebook as a sentence not an opportunity. The next killer product Facebook needs a year or two from now might never coalesce.

And if they do work hard, a culture of anxiety and paralysis will work against them. No one wants to code with their hands tied, and some would prefer a less scrutinized environment. Every decision will require endless philosophizing and risk-reduction. Product changes will be reduced to the lowest common denominator, designed not to offend or appear too tyrannical.

Source: Volkan Furuncu/Anadolu Agency + David Ramos/Getty Images

In fact, that’s partly how Facebook got into this whole mess. A leak by an anonymous former contractor led Gizmodo to report Facebook was suppressing conservative news in its Trending section. Terrified of appearing liberally biased, Facebook reportedly hesitated to take decisive action against fake news. That hands-off approach led to the post-election criticism that degraded morale and pushed the growing snowball of leaks down the mountain.

It’s still rolling.

How to stop morale’s downward momentum will be one of Facebook’s greatest tests of leadership. This isn’t a bug to be squashed. It can’t just roll back a feature update. And an apology won’t suffice. It will have to expel or reeducate the leakers and disloyal without instilling a witchunt’s sense of dread. Compensation may have to jump upwards to keep talent aboard like Twitter did when it was floundering. Its top brass will need to show candor and accountability without fueling more indiscretion. And it may need to make a shocking, landmark act of humility to convince employees its capable of change.

This isn’t about whether Facebook will disappear tomorrow, but whether it will remain unconquerable for the forseeable future.

Growth has been the driving mantra for Facebook since its inception. No matter how employees are evaluated, it’s still the underlying ethos. Facebook has poised itself as a mission-driven company. The implication was always that connecting people is good so connecting more people is better. The only question was how to grow faster.

Now Zuckerberg will have to figure out how to get Facebook to cautiously foresee the consequences of what it says and does while remaining an appealing place to work. “Move slow and think things through” just doesn’t have the same ring to it.


Read Full Article

Adobe Hikes the Price of Creative Cloud: Buy Now to Save Money

Clipisode launches a ‘talk show in a box’


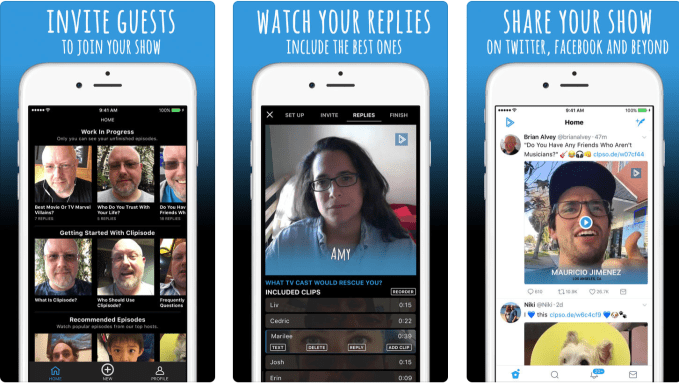
A company called Clipisode is today launching a new service that’s essentially a “talk show in a box,” as founder Brian Alvey describes it. Similar to how Anchor now allows anyone to build a professional podcast using simple mobile and web tools, Clipisode does this for video content. With Clipisode, you can record a video that can be shared across any platform – social media, the web, text messages – and collect video responses that can then be integrated into the “show” and overlaid with professional graphics.

The video responses feature is something more akin to a video voicemail-based call-in feature.

Here’s how it works. The content creator will first use Clipisode to record their video, and receive the link to share the video across social media, the web, or privately through email, text messaging, etc. When the viewer or guest clicks the link, they can respond to the question the show’s “host” posed.

For example, a reporter could ask for viewers’ thoughts on an issue or a creator could ask their fans what they want to see next.

How the video creator wants to use this functionality is really up to them, and specific to the type of video show they’re making.

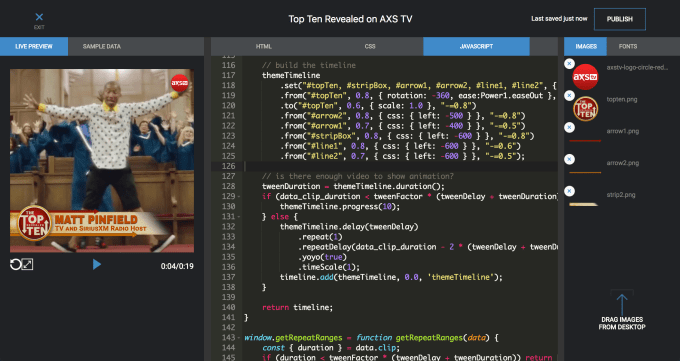
To give you an idea, during a pre-launch period, the app has been tested by AXS TV to promote their upcoming Top Ten Revealed series by asking music industry experts “Who Is Your All-time Favorite Guitarist?”

BBC Scotland asked their Twitter followers who they want to see hired as the new manager for the Scotland national football team.

A full-time Twitch gamer, Chris Melberger asked his subscribers what device they watch Twitch on.

The content creator can then receive all the video responses to these questions privately, choose which ones they want to include in their finished show, and drag those responses into the order they want. The creator can respond back to the clips, too, or just add another clip at the end of of their video. Uploading pre-recorded clips from services like Dropbox or even your phone is supported as well.

Plus, content creators can use Clipisode to overlay professional-looking animations and graphics on top of the final video with the responses and replies. This makes it seem more like something made with help from a video editing team, not an app on your phone.

Because Clipisode invitations are web links, they don’t require the recipients to download an app.

“[People] don’t want to download an app for a one-time video reply,” explains Alvey. “But with this, people can reply.” And, he adds, what makes Clipisode interesting from a technical perspective, is that the web links users click to reply can work in any app in a way that feels seamless to the end user.

“That’s our biggest trick – making this work in other people’s apps, so there’s no new social network to join and nothing to download,” he says.

The app is free currently, but the plan is to generate revenue by later selling subscription access to the authoring suite where users can create the animated overlays and branding components that give the video the professional look-and-feel.

In an online CMS, creators can author, test and deploy animated themes that run on top of their videos.

The final video product can be shared back to social media, or downloaded as a video file to be published on video-sharing sites, social media, or as a video podcast.

Clipisode has been in development for some time, Alvey says. The company originally raised less than a million from investors including Mike Jones and Mark Cuban for a different product the founder describes as a Patreon competitor, before pivoting to Clipisode. Investors funded the new product with less than half a million.

The app itself took a couple of years to complete, something that Alvey says has to do with the animation studio it includes and the small team. (It’s just him and technical co-founder Max Schmeling.)

Clipisode is a free download on iOS and Android.


Read Full Article